How an Application Becomes Vulnerable to PHP2Shell
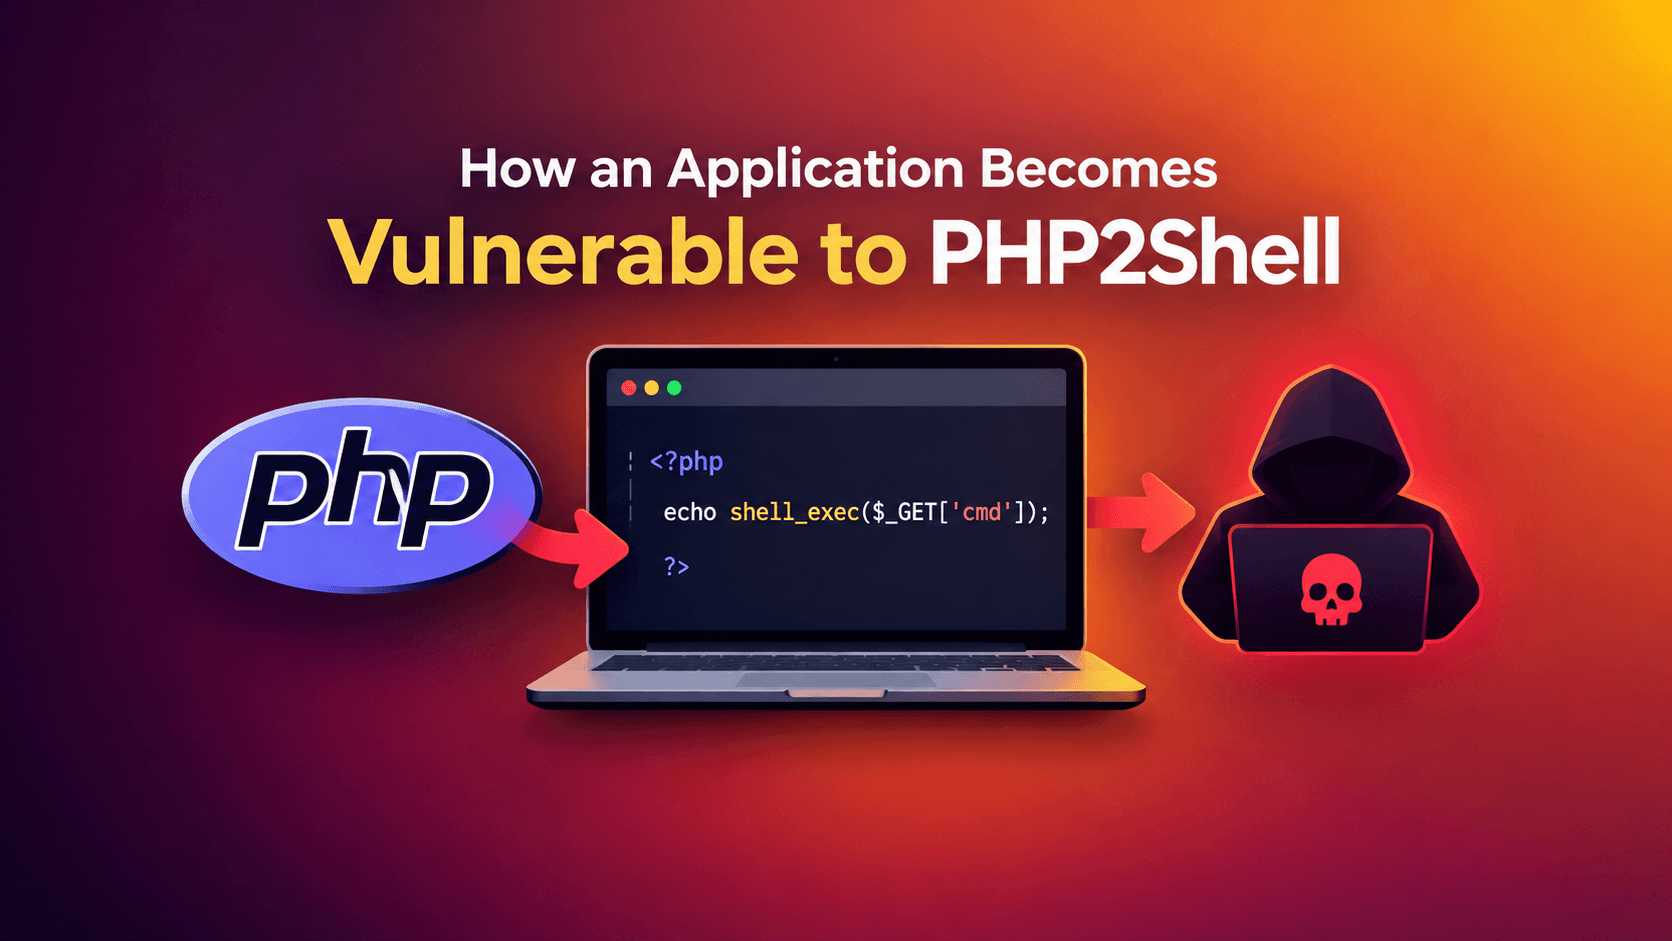
In October 2026 two critical vulnerabilities hit the PHP core. CVE-2026-109618 and CVE-2026-109619. Researchers nicknamed them PHP2Shell. The CVSS v4.0 score reached 9.2. That score sits near the top of the scale. These flaws allow remote code execution. No login is needed. No application bug is needed. The problem lives one layer below your code. PHP2Shell is not a flaw in your application. It lives inside PHP itself. The feature at fault is called session.upload_progress. Most developers never configure it by hand. If your server runs an unpatched PHP version and accepts file uploads you may be exposed. This holds true regardless of how carefully your own code was written. Good application security practices do not block this path.
0 Elliot
ElliotOct 26, 2026 00 7m